
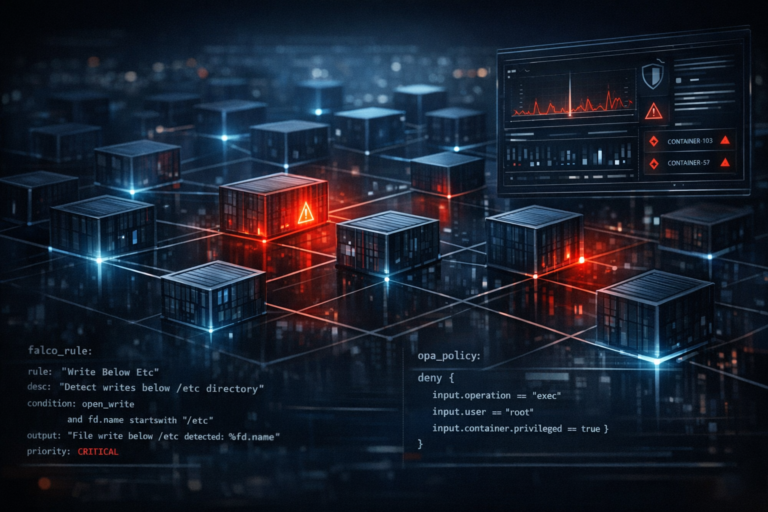
Learn to implement powerful runtime security policies for your containers on both Linux hosts and Kubernetes clusters. Dive into practical examples using Falco rules for behavioral threat detection and Open Policy Agent (OPA) for proactive enforcement, moving beyond basic vulnerability scanning.

Aspiring entrepreneurs often face a crucial fork in the road: building a business from scratch or buying an existing one. We dive into the common pitfalls and hidden advantages of each path, asking which strategy truly mitigates risk and accelerates success.
Attackers increasingly rely on subtle, often overlooked techniques to maintain access. This guide dives deep into uncovering sophisticated persistence mechanisms across both Windows and Linux, equipping engineers with methods to detect what typical scans miss.
Ruby for DevOps — Part 6 of 6 A fleet task looks deceptively simple: select the right hosts, run one […]
Dive deep into the raw power of operating system security events. Learn to build custom threat detection and response tools by directly interacting with Windows ETW and Linux Auditd, gaining unparalleled visibility and control beyond off-the-shelf agents.
Precise Process Isolation: Crafting Custom Sandbox Policies with Linux Seccomp and Windows AppLocker
Move beyond basic containerization to isolate critical services and untrusted scripts with surgical precision. Learn to leverage native OS features like Linux seccomp and Windows AppLocker for robust, fine-grained process sandboxing and execution control.
The definition of a "DevOps Engineer" seems to shift monthly. Are traditional roles disappearing, or are we just witnessing a critical evolution of skills? Let's discuss what truly matters in today's landscape.
Developers crave speed and innovation, while security teams demand rigor and compliance. This common organizational friction often slows down progress and creates tension. How do we move from conflict to collaboration, building secure software without sacrificing agility?
Discover how to integrate AI for deep analysis of your Infrastructure-as-Code to proactively identify subtle misconfigurations and security vulnerabilities. Learn to build a Ruby workflow for automated detection and remediation, preventing costly issues before deployment.
Go beyond static firewall rules. Learn to implement context-aware network egress filtering on Windows and Linux, preventing sophisticated data exfiltration with OS-native tools and advanced techniques.
Traditional disk forensics falls short against sophisticated in-memory threats. Learn practical, non-disruptive techniques to acquire and analyze live memory on Windows and Linux systems, uncovering stealthy rootkits and injected code without service interruption.